


The Vigor3912S model comes equipped with a 256GB SSD pre-installed with Ubuntu OS and Docker applications such as Suricata IDS (Intrusion Detection System) and VigorConnect to enhance network security.
**bi-directional(TX+RX) performance
Quad-Core Powerful Enterprise Gateway
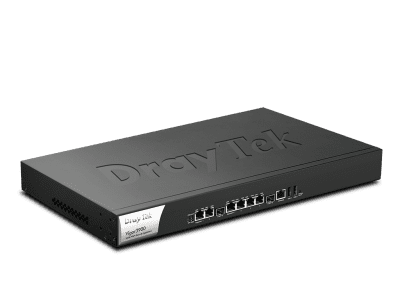
The Vigor3912 series Multi-WAN routers are high-performance enterprise-level broadband routers with 2 x 10Gb SFP+ Fibre configurable WAN/LAN slots, 2 x 2.5GbE configurable WAN/LAN ports, 4 x 1GbE configurable WAN/LAN ports, and 4 x 1GbE fixed LAN ports with 15.6 Gbps max. NAT throughput and Software Acceleration (bi-directional), 1,000k NAT sessions and other enterprise-level features. With the capacity to handle up to 500 VPN tunnels including 200 OpenVPN /SSL-VPN tunnels, and 100 IP subnets simultaneously, Vigor3912 routers are an excellent solution for network applications in corporations, organisations and governments.
The session-based Load Balance feature allows the aggregation of multiple WAN connections to provide a higher speed internet connection. In addition to the Load Balance and Failover multi-WAN functions, the Vigor3912 supports High Availability (Common Address Redundancy Protocol) with hardware redundancy to ensure 24/7 system uptime for all WAN interfaces.
The Central Management feature provides a centralised console to manage your network. It includes AP Management to configure and manage up to 50 DrayTek Access Points, and Switch Management to configure and manage up to 30 DrayTek VigorSwitches.
The Vigor3912S model comes equipped with a 256GB SSD which supports Linux with Docker applications such as Suricata IDS and VigorConnect. Together with this router’s capacity, these powerful applications eliminate the need for additional servers, enforcing security options at the door.
Smart Action

Smart Action allows predefined events to trigger predefined actions. Vigor users can pre-configure up to 64 event-to-action profiles. Actions, such as sending alerts, emails, removing a VPN profile, etc., can be programmed for events such as network conditions, occurrence counts, etc., associated with specified time and date.
Smart Action will act on these events:
- Send an alert email when CPU usage reaches 90%
- Disable VPN profile at a specified time
- Limit the access of a LAN server by Schedule
- Remove VPN User profile on a specified date
- Wake up the PC when the office hours start
- Log Keyword Match (syslog log, console log, Suricata log) for Vigor3912S only
Linux Applications (Vigor3912S Only)
The Vigor3912S model comes equipped with a 256GB SSD pre-installed with Ubuntu OS and Docker applications such as Suricata IDS and VigorConnect to enhance network security:
- VigorConnect
- Suricata
- Applications on Ubuntu


Linux Application – VigorConnect (Vigor3912S Only)
The Vigor3912S router supports Docker applications such as VigorConnect directly on the device. This capability simplifies network management by allowing VigorConnect to monitor DrayTek devices without requiring an additional computer. The installation process is straightforward and can be completed through the router’s web user interface (WUI) with just a few clicks. This feature provides a convenient and efficient solution for network administrators to oversee and manage their network infrastructure.

Linux Application – Suricata (Vigor3912S Only)
A popular open-source threat detection application for detecting and preventing a wide range of network threats.
The Vigor3912S is pre-installed with the Linux-based application Suricata, an open-source threat detection system that supports more than 60,000 rules, including 6,000+ CVE (Common Vulnerabilities and Exposures) rules, and it can detect and prevent a wide range of network threats, such as malware, network intrusions, denial-of-service attacks and data breaches.
Suricata, an intrusion detection system (IDS), monitors LAN and WAN traffic through the router. A log is generated if any unusual activity is detected, which can be sent to the network administrator via the router’s Web Notification function.

Blocking can be achieved with the “Smart Action” feature in the router.
This feature monitors network traffic and detect malicious activity in real time. Suricata works by analysing packets and comparing them to a set of rules to determine whether the traffic is legitimate. If it detects suspicious activity, it can raise an alarm. Suricata is highly customisable and can monitor many network environments, from small homes to large enterprise networks.
Suricata – The Threat Log Generator

Suricata Features (Vigor3912S Only)
Statistical Graph
Suricata Statistical Graph presents the timing and frequency of threats. When the mouse hovers over the point representing the most frequent threat, a small menu will pop up to display the number of occurrences of that threat. Additionally, a click on the item will display more details that are crucial for security enhancement.

Notifications via Smart Action
When Suricata detects a threat, the Vigor3912S can alert administrators through Smart Action using the following methods:
- Web Notification – Alerts are displayed directly within the router’s web interface, ensuring administrators see notifications immediately upon login.
- Telegram Notification – Alerts can be delivered to a designated Telegram account, enabling real-time notifications on mobile devices.
These notification options ensure that administrators are promptly informed of potential security threats, allowing faster incident response and improved network protection.


Auto-Blocking with Smart Action
When Suricata detects a network threat, Smart Action can automatically apply advanced filtering and blocking rules. Administrators define specific threat-related keywords in the Smart Action profile. If an event detected by Suricata matches one of these predefined keywords, the Vigor3912S will immediately block the associated IP address.
This proactive and automated response mechanism strengthens network security by mitigating threats in real-time without requiring constant manual intervention from administrators.

** bi-directional(TX+RX) performance
Interface

*WAN/LAN Switchable
- 2 x USB 3.0 ports for external storage (one USB flash drive is supported at any one time)
- Factory Reset Button
- RJ-45 Console Port
- 2 x 10G/2.5G/1G SFP+ Fibre configurable WAN/LAN Slots*
- 2 x 2.5G/1G/100M/10M Ethernet configurable WAN/LAN ports*
- 4 x 1G/100M/10M Ethernet Configurable WAN/LAN ports*
- 4 x 1G/100M/10M Ethernet LAN ports with 1 million NAT sessions
*WAN/LAN Switchable
Performance Comparison: Vigor3912 vs. Vigor3910
NAT throughput (1.9x times faster)
IPSec throughput
(2.1 times faster)
SSL-VPN throughput
(2.9 times faster)
Wireguard throughput
(3.2 times faster)
**bi-directional(TX+RX) performance
Maximise Performance with Fast NAT and Fast Routing
Enhance overall network performance with optimised data packet processing and forwarding. This feature improves network efficiency by improving transmission speed, and enhances user experience by minimising network latency, making it ideal for real-time applications such as large file transfers and voice calls.

Key Features

EasyVPN

Port Knocking for VPN service

Quad-Core Processor
Offers excellent performance for bandwidth-demanding enterprise networks.

Hotspot Web Portal

10G SFP+
Provides 2 x 10G-capable fibre SFP ports for WAN or LAN connection.

Bandwidth Management
Control Internet bandwidth usage by users by using the bandwidth limit and session limit policy settings, and prioritise traffic by using the QoS feature.

Load Balancing

Firewall & Content Filter
Use URL keywords or web categories to filter web pages and block access to insecure or inappropriate content.

VPN (Virtual Private Network)
Build a secure and private tunnel from the LAN of Vigor3912 to the remote offices and teleworkers over the Internet. Learn more

DrayDDNS

SSL VPN

Central AP Management
Use the Vigor3912 router as a wireless controller to maintain and monitor the VigorAPs. Learn more

PPPoE Server

Central Switch Management

VPN 2FA Auth for AD/LDAP
Enhance the security for remote VPN connections and eliminate the cost for an official authentication system. Learn more

VPN Matcher

VRRP
Keep network running by automatically switching to a backup router if the primary fails.
[DISPLAY OFF] —– MOBILE VIEW
EasyVPN
Secure VPN in Seconds: No Keys, No Configs, Just Login.
Port Knocking for VPN service
Quad-Core Processor
Offers excellent performance for bandwidth-demanding enterprise networks.
Hotspot Web Portal
10G SFP+
Provides 2 x 10G-capable fibre SFP ports for WAN or LAN connection.
Bandwidth Management
Control Internet bandwidth usage by users by using the bandwidth limit and session limit policy settings, and prioritise traffic by using the QoS feature.
Load Balancing
Firewall & Content Filter
Use URL keywords or web categories to filter web pages and block access to insecure or inappropriate content.
VPN (Virtual Private Network)
Build a secure and private tunnel from the LAN of Vigor3912 to the remote offices and teleworkers over the Internet. Learn more
DrayDDNS
SSL VPN
Central AP Management
Use the Vigor3912 router as a wireless controller to maintain and monitor the VigorAPs. Learn more
PPPoE Server
Central Switch Management
VPN 2FA Auth for AD/LDAP
Enhance the security for remote VPN connections and eliminate the cost for an official authentication system. Learn more
VPN Matcher
VRRP
Fibre to the Building/Home
The Vigor3912 is an ideal choice for tier 2/3 ISPs and co-working spaces
High Performance with 10Gb SFP+
For both NAT and routing network, and for both 10Gb-WAN and 10Gb-LAN, Vigor3912 is ready to deliver high throughput to your business.
Layer 3 Routing with BGP and OSPF
With the most popular Exterior and Interior Gateway Protocols, Vigor3912 is ideal for ISP deployment.
Layer 2 Security with PPPoE Server and VLAN
With 200 PPPoE user accounts and 100 VLAN/LAN subnets, the Vigor3912 provides 15.6 Gbps (bi-directional; TX+RX) NAT throughput, making network infrastructure segmentation secure and easy.

Configurable WAN/LAN Ports
12 Ports in total
8 ports from a total of 12 ports, can be configured as either a LAN port or a WAN interface. For example, the following port options are achievable:
- 8 x WAN interfaces and 4 x LAN Ports or
- 1 x WAN interface and 11 LAN Ports

Server Load Balancing
For organisations that host multiple servers in their network, a policy of server load balance can be configured, such that the router can distribute the inbound NAT sessions evenly for the servers based on the configured load balance weight. This will avoid excessive load on a single server, prevent server failure due to overloading, and optimise resource usage.

URL Reputation
URL Reputation is a cloud-based threat intelligence service that adds an extra layer of security to protect LAN clients during their online activities.
With a total of 82 content categories, including 10 security-focused ones, it provides comprehensive and up-to-date protection for both home and business networks.
These categories cover a wide range of areas—from malware, spyware, and adware, to parental controls, business productivity, and social networking—helping to create a safer online environment, enhance employee productivity, and support efficient bandwidth management.

IP Reputation
Every internet communication involves source and destination IP addresses. Cybercriminals often exploit known malicious IPs to launch attacks using various techniques, including:
- Botnets
- TOR nodes and anonymous proxies
- Command-and-Control (C2) servers
- Phishing servers
- Distributed Denial of Service (DDoS) attacks

IP Reputation helps identify and block traffic from these high-risk IP addresses, adding an essential layer of network protection against cyber threats.
Blocking communication with malicious IP addresses is critical for network security. However, relying on static blocklists is no longer effective, as they lack the real-time, predictive intelligence needed to combat evolving threats. The IP Reputation Service addresses this challenge by delivering dynamic, real-time scoring and classification of IP addresses. It enables the automatic blocking of:
- High-risk traffic
- Suspicious proxies
- Malware distributors
- IPs associated with recent malicious activity
The system evaluates IPs based on multiple factors, including infection history, protocol behaviour, and attack frequency. Each IP is assigned a reputation score, which determines whether it should be trusted, monitored, or blocked, ensuring proactive and intelligent network protection.
Advanced VPN Features

VPN from LAN
This feature offers a more secure method for connecting to servers by restricting LAN clients’ access to LAN servers through a VPN only. This ensures that data transmission between LAN clients and servers is encrypted, protecting critical data and enhancing overall security.
VPN User Isolation
Activating a VPN connection to access a company’s internet for work has become a common routine for many employees.
Teleworkers need to connect to the company’s servers through VPN connections. However, it is often unnecessary for VPN users to access each other, which may pose security risks. By enabling the “Isolate VPN Users from each other” option, you can ensure that each VPN user is isolated and the VPN network is more secure.


2FA with AD/LDAP Server
Enhance the security of remote dial-in VPN connections with two-factor authentication integrated with AD/LDAP servers. DrayTek offers various authentication methods, including TOTP, email, SMS, and URL links. This approach not only adds an extra layer of security but also helps reduce costs associated with SMS messages and official authentication system license fees.
Packet Capture Tool for VPN Tunnel
By either mirroring all packets to a designated LAN port or VPN connection, whether LAN to LAN profiles or remote Dial-in users, or even downloading PCAP files via WUI remotely, spotting an issue is easier than ever.

Effortless and Secure VPN Access with EasyVPN
Setting up a VPN can often be complex, involving protocol selection, manual configurations, and troubleshooting, especially for non-technical users. While Vigor routers support advanced VPN protocols such as IPsec, WireGuard, and OpenVPN, traditional setup methods can be time-consuming and daunting.
EasyVPN simplifies this process by offering a streamlined, hassle-free solution for secure remote connectivity. With EasyVPN, users can quickly establish encrypted connections without the need to:
- Manually generate WireGuard keys
- Import OpenVPN configuration files
- Upload certificates
By automating these steps, EasyVPN delivers a fast, secure, and intuitive VPN experience—perfect for businesses and users who want robust protection without the technical complexity.

Stealth Security Protection with Port Knocking
DrayTek’s Port Knocking technology adds an advanced stealth security layer by keeping critical network services completely invisible to unauthorised users. Instead of exposing management ports or VPN services to the public internet, Port Knocking requires a predefined “knock” sequence before access is granted, ensuring that only trusted users can discover and use these services.
By integrating three powerful functions, Port Knocking provides robust protection against port scanning, brute-force attacks, and unauthorised access.
Port Redirection
- Conceal real service ports from the public internet
- Redirect unauthorised requests to non-existent services to prevent detection

Secure Router Management Access
- Allow router management access only after a successful knock sequence or through a secure internal server
- Completely eliminate direct exposure of the management interface to the open internet
VPN Service Control (WAN Binding)
- Keep VPN services invisible until the correct knock sequence is received
- Bind VPN availability to specific WAN interfaces and authorised IP addresses
How It Works
- By default, all protected ports remain closed and undetectable
- After the correct knock sequence is received, selected ports open temporarily for authorised access
- Once the configured time window expires, services automatically return to hidden mode
With DrayTek Port Knocking, your network operates in stealth mode, invisible to attackers yet instantly accessible to authorised administrators and remote users. It is the ideal solution for organisations that demand high-level security without compromising accessibility.
All-in-One Management
Vigor routers provide a management platform for Vigor devices on the LAN
Auto-Discovery
Automatically discover LAN subnets and add detected VigorSwitches/APs into the managed list.
Provisioning
Most-frequently used settings can be pre-defined on the Vigor Router, which can then be provisioned to the managed VigorSwitch/AP.
Monitoring
Vigor Routers provide a centralised view of managed devices so you can always check if the managed Vigor Switch/AP is online.
System Maintenance
Support basic maintenance remotely via Vigor Router, such as remote reboot, factory reset, configuration backup/restore.

Auto-Discovery
Automatically discover LAN subnets and add detected VigorSwitches/APs into the managed list.
Provisioning
Most-frequently used settings can be pre-defined on the Vigor Router, and then provisioned to the managed VigorSwitch/AP.
Monitoring
The Vigor Router provides a centralised view of managed devices, so you can always check if the managed Vigor Switch/AP is online.
System Maintenance
Support basic maintenance remotely via Vigor Router, such as remote reboot, factory reset, configuration backup/restore.
Management Solution
| Software Management |
|---|
VigorACS 3

- Zero Touch Deployment & Provisioning
- Auto VPN
- Interface Quality & SLA
- VoIP Optimisation & Monitoring
- Application Visibility
- Application Based SD-WAN Policy
- Customised Hotspot Page with Multilingual Support
- Hotspot Clients Analytics
- ACS Server Load Balancing / Failover
[DISPLAY OFF] —– MOBILE VIEW
VigorACS 3
- Zero Touch Deployment & Provisioning
- Auto VPN
- Interface Quality & SLA
- VoIP Optimisation & Monitoring
- Application Visibility
- Application Based SD-WAN Policy
- Customised Hotspot Page with Multilingual Support
- Hotspot Clients Analytics
- ACS Server Load Balancing / Failover
| All-in-One Management |
|---|
Vigor Router SWM

- Auto-Discovery
- Provisioning
- Monitoring
- Centralised Hierarchy View
- Reboot PoE Devices Remotely
- Quick VLAN Configuration
VigorAP-based APM

- Auto-Discovery
- Auto-Provisioning
- Monitoring
- Centralised View
- Alarm
- Reboot VigorAP Remotely
- Wi-Fi Client Load Balancing
[DISPLAY OFF] —– MOBILE VIEW
Vigor Router SWM
- Auto-Discovery
- Provisioning
- Monitoring
- Centralized Hierarchy View
- Reboot PoE Devices Remotely
- Quick VLAN Configuration
VigorAP-based APM
- Auto-Discovery
- Auto-Provisioning
- Monitoring
- Centralized View
- Alarm
- Reboot VigorAP Remotely
- Wi-Fi Client Load Balancing
In-the-Box

Vigor3912

Rack Mount Kit
(brackets)

Console Connector +
Console Flat Cable

RJ-45 Cable
(Ethernet)

Power Cord

Quick Start Guide
Models Comparison Chart
| Vigor3912S | Vigor3912 | Vigor3910 | Vigor3900 | |
|---|---|---|---|---|
| Products |  | |  |  |
| Configurable WAN/LAN Port | 2 x 10 Gigabit SFP+ 2 x 2.5GbE RJ-45 4 x GbE RJ-45 | 2 x 10 Gigabit SFP+ 2 x 2.5GbE RJ-45 4 x GbE RJ-45 | 2 x 10 Gigabit SFP+ 2 x 2.5GbE RJ-45 4 x GbE RJ-45 | |
| Fixed WAN Port | 4 x GbE RJ-45 1 x SFP | |||
| Fixed LAN Port | 4 x GbE RJ-45 | 4 x GbE RJ-45 | 4 x GbE RJ-45 | 2 x GbE RJ-45 1 x SFP |
| USB Port | 2 x USB 3.0 | 2 x USB 3.0 | 2 x USB 3.0 | 2 x USB 2.0 |
| Console Port | 1 x RJ-45 | 1 x RJ-45 | 1 x RJ-45 | 1 x RJ-45 |
| Memory | 8GB DDR4 | 8GB DDR4 + 256GB SSD | ||
| NAT Throughput | 15.6 Gbps (Hardware acceleration is built-in) | 15.6 Gbps (Hardware acceleration is built-in) | 9.4 Gbps (Hardware acceleration is built-in) | 950 Mbps |
| IPsec VPN Performance | 5.7 Gbps (AES 256 bits) | 5.7 Gbps (AES 256 bits) | 3.3 Gbps (AES 256 bits) | 900 Mbps (AES 256 bits) |
| Max. Number of NAT Sessions | 1000k | 1000k | 150k | 120k |
| Max. concurrent VPN Tunnels | 500 | 500 | 500 | 500 |
| Max. concurrent SSL VPN | 200 | 200 | 200 | 100 |
| VPN Trunk and Backup | ||||
| WAN Backup/Failover | ||||
| WAN Load Balancing | ||||
| DrayDDNS | ||||
| Tagged VLAN | ||||
| Max. Number of VLAN | 100 | 100 | 100 | 50 |
| Hotspot Web Portal | ||||
| BGP Routing | ||||
| High Availability | ||||
| Firewall | ||||
| Content Filtering | ||||
| Bandwidth Management | ||||
| VoIP Prioritization | ||||
| Configurable Port | ||||
| Built-in Event Data Record | ||||
| Plain Text Config File | ||||
| Managed via VigorACS 3 | (after V4.3.5.1) | (after V3.9.2) | (after V3.9.2) | |
| Central AP Management | 50 | 50 | 50 | 50 |
| Central Switch Management | 30 | 30 | 30 | 20 |
| Central VPN Management | 16 |
[DISPLAY OFF] —– MOBILE VIEW —- Vigor3912S
| Vigor3912S |
|---|
 |
[DISPLAY OFF] —– MOBILE VIEW —- Vigor3912
| Vigor3912 |
|---|
|
[DISPLAY OFF] —– MOBILE VIEW —- Vigor3910
| Vigor3910 |
|---|
 |
[DISPLAY OFF] —– MOBILE VIEW —- Vigor3900
| Vigor3900 |
|---|
 |
Vigor391x Series Models Comparison
| Model | Vigor3912S | Vigor3912 | Vigor3910 |
|---|---|---|---|
| Product | | | |
| Multi Gigabit WAN | 2 x 10Gb SFP+ WAN/LAN slots 2 x 2.5GbE WAN/LAN ports 4 x 1GbE WAN/LAN ports | 2 x 10Gb SFP+ WAN/LAN slots 2 x 2.5GbE WAN/LAN ports 4 x 1GbE WAN/LAN ports | 2 x 10Gb SFP+ WAN/LAN slots 2 x 2.5GbE WAN/LAN ports 4 x 1GbE WAN/LAN ports |
| Gigabit LAN | 4 | 4 | 4 |
| Quad-Core Processor | 2GHz | 2GHz | 1.2GHz |
| Max. Number of VLAN | 100 | 100 | 100 |
| VPN Tunnels | 500 | 500 | 500 |
| Memory | 8GB DDR4 + 256GB SSD | 4GB DDR4 | |
| Wireless LAN |
Specifications
Interface [Display None]
| Interface | |
|---|---|
| WAN/LAN Port | 2 x 10G/2.5G/1G SFP+ Fibre configurable WAN/LAN Slots 2 x 2.5G/1G/100M/10M Ethernet configurable WAN/LAN, RJ-45 4 x 1G/100M/10M Ethernet Configurable WAN/LAN ports, RJ-45 4 x 1G/100M/10M Ethernet LAN ports with 1 million NAT sessions |
| USB Port | 2 x USB 3.0 ports for external storage (one USB flash drive is supported at any one time) |
| Console Port | 1 x RJ-45 |
| Reset Button | 1 x Factory Reset |
[DISPLAY OFF] —– MOBILE VIEW
| Interface |
|---|
| WAN/LAN Port: 2 x 10G/2.5G/1G SFP+ Fibre configurable WAN/LAN Slots 2 x 2.5G/1G/100M/10M Ethernet configurable WAN/LAN, RJ-45 4 x 1G/100M/10M Ethernet Configurable WAN/LAN ports, RJ-45 4 x 1G/100M/10M Ethernet LAN ports with 1 million NAT sessions |
| USB Port: 2 x USB 3.0 ports for external storage (one USB flash drive is supported at any one time) |
| Console Port: 1 x RJ-45 |
| Reset Button: 1 x Factory Reset |
Performance [Display None]
| Performance | |
|---|---|
| NAT Throughput | 15.6 Gbps ( bi-directional(TX+RX) performance) |
| IPsec VPN Performance | 5.7 Gbps |
| SSL VPN Performance | 4.3 Gbps |
| NAT Sessions | 1,000,000 |
| Max. Concurrent VPN Tunnels | 500 |
| Max. Concurrent OpenVPN + SSL VPN | 200 |
[DISPLAY OFF] —– MOBILE VIEW
| Performance |
|---|
| NAT Throughput: 15.6 Gbps ( bi-directional(TX+RX) performance) |
| IPsec VPN Performance: 5.7 Gbps (AES 256 bits) |
| SSL VPN Performance: 4.3 Gbps |
| Max. Number of NAT Sessions: 1000,000 |
| Max. Concurrent VPN Tunnels: 500 |
| Max. Concurrent OpenVPN + SSL VPN: 200 |
Internet Connection [Display None]
| Internet Connection | |
|---|---|
| IPv4 | PPPoE, DHCP, Static IP |
| IPv6 | PPP, DHCPv6, Static IPv6, TSPC, AICCU, 6rd, 6in4 Static Tunnel |
| 802.1p/q Multi-LAN Tagging | |
| Multi-VLAN/PVC | |
| Load Balancing | IP-based, Session-based |
| WAN Active on Demand | Link Failure, Traffic Threshold |
| Connection Detection | ARP, Ping, Strict ARP |
| WAN Data Budget | |
| Dynamic DNS | |
| DrayDDNS | |
[DISPLAY OFF] —– MOBILE VIEW
| Internet Connection | |
|---|---|
| IPv4: PPPoE, DHCP, Static IP, PPTP/L2TP | |
| IPv6: PPP, DHCPv6, Static IP, TSPC, AICCU, 6rd, 6in4 Static Tunnel | |
| 802.1p/q Multi-VLAN Tagging | |
| Multi-VLAN/PVC | |
| 3G/4G/LTE WAN with USB modem | |
| WAN Failover | |
| Connection Detection: ARP, Ping, Strict ARP | |
| WAN Data Budget | |
| Dynamic DNS | |
| DrayDDNS | |
LAN Management [Display None]
| LAN Management | |
|---|---|
| VLAN | 802.1q Tag-based, Port-based |
| Max. Number of VLAN | 100 |
| Number of LAN Subnet | 100 |
| DHCP Server | Multiple IP Subnet, Custom DHCP Options, Bind-IP-to-MAC |
| LAN IP Alias | |
| IP Pool Count | Up to 4K per LAN Subnet |
| PPPoE Server | |
| Port Mirroring | |
| Local DNS Server | |
| Conditional DNS Forwarding | |
| Hotspot Web Portal (Profile No.) | 4 |
| Hotspot Authentication | Click-Through, Social Login, SMS PIN, RADIUS, External Portal Server |
[DISPLAY OFF] —– MOBILE VIEW
| LAN Management | |
|---|---|
| VLAN: 802.1q Tag-based, Port-based | |
| Max. Number of VLAN: 100 | |
| Number of LAN Subnet: 100 | |
| DHCP Server: Multiple IP Subnet, Custom DHCP Options, Bind-IP-to-MAC | |
| LAN IP Alias | |
| IP Pool Count: Up to 4K per LAN Subnet | |
| PPPoE Server | |
| Port Mirroring | |
| Local DNS Server | |
| Conditional DNS Forwarding | |
| Hotspot Web Portal (Profile No.) | 4 |
| Hotspot Authentication: Click-Through, Social Login, SMS PIN, RADIUS, External Portal Server | |
Networking [Display None]
| Networking | |
|---|---|
| Routing | IPv4 Static Routing, IPv6 Static Routing, Policy Route, Inter-VLAN Routing, Fast Routing, RIP v1/v2, OSPFv2, BGP |
| Policy-based Routing | Protocol, IP Address, Port, Domain, Country |
| Smart Action | |
| High Availability | |
| DNS Security (DNSSEC) | IGMP v2/v3, IGMP Proxy, IGMP Snooping & Fast Leave |
| Local RADIUS server | |
[DISPLAY OFF] —– MOBILE VIEW
| Networking | |
|---|---|
| Routing: IPv4 Static Routing, IPv6 Static Routing, Policy Route, Inter-VLAN Routing, Fast Routing, RIP v1/v2, BGP, OSPFv2 | |
| Policy-based Routing: Protocol, IP Address, Port, Domain, Country | |
| Smart Action | |
| High Availability | |
| DNS Security (DNSSEC) | |
| IGMP: IGMP v2/v3, IGMP Proxy, IGMP Snooping & Fast Leave | |
| Local RADIUS server | |
VPN [Display None]
| VPN | |
|---|---|
| LAN-to-LAN | |
| Teleworker-to-LAN | |
| EasyVPN | |
| Port Knocking | |
| Protocols | PPTP, L2TP, IPsec, L2TP over IPsec, SSL, GRE, IKEv2, IPsec-XAuth, OpenVPN, Wireguard |
| IPsec VPN Throughput (AES 256 bits) (single-directional) | 3300 Mbps |
| IPsec VPN Throughput (AES 256 bits) (bi-directional) | 5700 Mbps |
| SSL VPN Throughput (single-directional) | 3300 Mbps |
| SSL VPN Throughput (bi-directional) | 4300 Mbps |
| Wireguard VPN Throughput (single-directional) | 900 Mbps |
| Wireguard VPN Throughput (bi-directional) | 1080 Mbps |
| User Authentication | Local, RADIUS, LDAP, TACACS+, mOTP, TOTP |
| IKE Authentication | EAP, Pre-Shared Key, X.509, XAuth |
| IPsec Authentication | MD5, SHA-1, SHA-256, SHA-512 |
| Encryption | MPPE, DES, 3DES, AES |
| VPN Trunk (Redundancy) | Load Balancing, Failover |
| Single-Armed VPN | |
| NAT-Traversal (NAT-T) | |
| VPN from LAN | |
| VPN Isolation | |
| VPN Packet Capture | |
| VPN 2FA Authentication for AD/LDAP | |
| DrayTek VPN Matcher | |
[DISPLAY OFF] —– MOBILE VIEW
| VPN | |
|---|---|
| LAN-to-LAN | |
| Teleworker-to-LAN | |
| EasyVPN | |
| Port Knocking | |
| Protocols: PPTP, L2TP, IPsec, L2TP over IPsec, SSL, GRE, IKEv2, IPsec-XAuth, OpenVPN, Wireguard | |
| IPsec VPN Throughput (AES 256 bits) (single-directional): 3300 Mbps | |
| IPsec VPN Throughput (AES 256 bits) (bi-directional): 5700 Mbps | |
| SSL VPN Throughput (single-directional): 3300 Mbps | |
| SSL VPN Throughput (bi-directional): 4300 Mbps | |
| Wireguard VPN Throughput (single-directional): 900 Mbps | |
| Wireguard VPN Throughput (bi-directional): 1080 Mbps | |
| User Authentication: Local, RADIUS, LDAP, TACACS+, mOTP, TOTP | |
| IKE Authentication: EAP, Pre-Shared Key, X.509, XAuth | |
| IPsec Authentication: MD5, SHA-1, SHA-256, SHA-512 | |
| Encryption: MPPE, DES, 3DES, AES | |
| VPN Trunk (Redundancy): Failover, Load Balancing | |
| Single-Armed VPN | |
| NAT-Traversal (NAT-T) | |
| VPN from LAN | |
| VPN Isolation | |
| VPN Packet Capture | |
| VPN 2FA Authentication for AD/LDAP | |
| DrayTek VPN Matcher | |
Firewall & Content Filtering [Display None]
| Firewall & Content Filtering | |
|---|---|
| IP-based Firewall Policy | |
| Content Filtering | Application, URL Keyword, DNS Keyword, Web Features, Web Category (subscription required) |
| DoS Attack Defense | |
| Spoofing Defense | |
[DISPLAY OFF] —– MOBILE VIEW
| Firewall & Content Filtering | |
|---|---|
| IP-based Firewall Policy | |
| Content Filtering: Application, URL Keyword, DNS Keyword, Web Features, Web Category (subscription required) | |
| DoS Attack Defence | |
| Spoofing Defense | |
Linux Applications[Display None]
| Linux Applications (Vigor3912S only) | |
|---|---|
| Suricata | |
| VigorConnect | |
[DISPLAY OFF] —– MOBILE VIEW
| Linux Applications (Vigor3912S only) | |
|---|---|
| Suricata | |
| VigorConnect | |
NAT [Display None]
| NAT | |
|---|---|
| NAT | Port Redirection, Open Ports, Port Triggering, Port Knocking, Fast NAT, DMZ Host, UPnP, Server Load Balance |
| ALG (Application Layer Gateway) | SIP, RTSP, FTP, H.323 |
| VPN Pass-Through | PPTP, L2TP, IPsec |
[DISPLAY OFF] —– MOBILE VIEW
| NAT | |
|---|---|
| NAT: Port Redirection, Open Ports, Port Triggering, Port Knocking Fast NAT, DMZ Host, UPnP, Server Load Balance | |
| ALG: (Application Layer Gateway) SIP, RTSP, FTP, H.323 | |
| VPN Pass-Through: PPTP, L2TP, IPsec |
Bandwidth Management [Display None]
| Bandwidth Management | |
|---|---|
| IP-based Bandwidth Limit | |
| IP-based Session Limit | |
| QoS (Quality of Service) | TOS, DSCP, 802.1p, IP Address, Service Type |
| VoIP Prioritization | |
| APP QoS | |
[DISPLAY OFF] —– MOBILE VIEW
| Bandwidth Management | |
|---|---|
| IP-based Bandwidth Limit | |
| IP-based Session Limit | |
| QoS (Quality of Service): TOS, DSCP, 802.1p, IP Address, Service Type | |
| VoIP Prioritization | |
| APP QoS | |
Management [Display None]
| Management | |
|---|---|
| Local Service | HTTP, HTTPS, Telnet, SSH v2, FTP, TR-069 |
| Port knocking for Local Service | |
| Config Backup/Restore | |
| Firmware Upgrade | TFTP, HTTP, TR-069 |
| 2-Level Administration Privilege | |
| Access Control | Access List, Brute Force Protection |
| Notification Alert | SMS, E-mail |
| SNMP | v1, v2c, v3 |
| Syslog | |
| Central AP Management | 50 Vigor Access Points |
| Central Switch Management | 30 Vigor Switches |
| VigorACS Management (Since f/w) | V4.3.5.1 |
[DISPLAY OFF] —– MOBILE VIEW
| Management | |
|---|---|
| Local Service: HTTP, HTTPS, Telnet, SSH v2, FTP, TR-069 | |
| Port Knocking for Local Service | |
| Config Backup/Restore | |
| Firmware Upgrade: TFTP, HTTP, TR-069 | |
| 2-Level Administration Privilege | |
| Access Control: Access List, Brute Force Protection | |
| Notification Alert: SMS, E-mail | |
| SNMP: v1, v2c, v3 | |
| Syslog | |
| AP Management: 50 VigorAPs | |
| Switch Management: 30 VigorAPs | |
| VigorACS Management: V4.3.5.1 (Since f/w) | |
Physical [Display None]
| Physical | |
|---|---|
| Power Input | AC 100~240V @ 0.6A |
| Max. Power Consumption | 35 watts |
| Memory | 8GB DDR4 (Vigor3912) 8GB DDR4 + 256GB SSD (Vigor3912S) |
| Dimension | 443 mm x 285 mm x 45 mm |
| Weight | 3.35 kg |
| Operating Temperature | 0 to 45°C |
| Storage Temperature | -10 to 55°C |
| Operating Humidity (non-condensing) | 10 to 90% |
[DISPLAY OFF] —– MOBILE VIEW
| Physical | |
|---|---|
| Power Input: AC 100~240V @ 0.6A | |
| Max. Power Consumption: 35 watts | |
| Memory: 8GB DDR4 (Vigor3912) 8GB DDR4 + 256GB SSD (Vigor3912S) | |
| Dimension: 443 mm x 285 mm x 45 mm | |
| Weight: 3.35 kg | |
| Operating Temperature: 0 to 45°C | |
| Storage Temperature: -10 to 55°C | |
| Operating Humidity (non-condensing): 10 to 90% |
Note :
- All specifications are subject to change without notice.
- The throughput figures are maximum, based on DrayTek internal testing with optimal conditions. The actual performance may vary depending on the different network conditions and applications activated.
Reviews
DrayTek Vigor2135ax Review Published in APC Magazine Issue 523 – Sep 2023


