


Note
- For SOS/ROC compatibility use firmware Vigor2765_v4.4.1_MDM2 or Vigor2765_v4.4.1_MDM4.
- SOS/ROC settings are enabled by default in this firmware.
NBN VDSL2 Connection Update
For current DrayTek VDSL2 router models, such as the Vigor2765 and Vigor2865 series to support the new NBN’s SOS/ROC functions. While current firmware support the bidirectional dynamic SRA function, you will need to execute a telnet command to upgrade to the SOS/ROC function.
A new firmware that enable the SOS/ROC function by default will be available by March 2022. (Read more…)
Dual-WAN VDSL2, 2.5GbE & Wi-Fi 6 VPN Security Routers
The Vigor2767 series supports VDSL2 35b (Supervectoring) connections, and one of its four Gigabit Ethernet LAN ports can be configured as a 2.5GbE WAN/LAN interface, enabling connectivity to any Ethernet-based broadband service.
With both integrated xDSL and a high-speed 2.5GbE Ethernet WAN port, the Vigor2767 series is compatible with all major internet technologies, including FTTP, FTTC, FTTB/N, HFC, Satellite, and Fixed Wireless services deployed by nbn™ in Australia and UFB in New Zealand.
Designed for both domestic and SMB environments, the router incorporates advanced security and networking features such as an object-oriented SPI Firewall, Content Security Management (CSM), URL/IP Reputation filtering, Port Knocking, support for up to 16 VPN tunnels, and dual USB ports for 4G LTE mobile broadband backup, printer sharing, or network storage.
The Vigor2767ax model features 802.11ax (Wi-Fi 6, AX3000) wireless technology, delivering combined speeds of up to 2976 Mbps (574 Mbps on 2.4 GHz and 2402 Mbps on 5 GHz). Business-grade wireless enhancements, including AirTime Fairness, Router-Assisted Roaming, and Band Steering, ensure reliable connectivity for bandwidth-intensive applications such as HD video streaming, online gaming, and VoIP.
Interface

(ax model)
- WLAN/WPS Button (ax model)
- Reset Button
- Fixed WAN Port: 1 x RJ-11
(For VDSL 35b/ADSL2+ WAN) - LAN/WAN Switchable Port: 1 x 2.5GbE RJ-45
- Fixed LAN Port: 3 x GbE RJ-45
- 2 x USB 2.0
- Power On/Off Switch
- Power Input
- Wi-Fi Antenna (ax model)
Key Features

2.5GbE
Provides higher performance to Wi-Fi 6 AP and other Ethernet devices.

35b Supervectoring Modem
Integrated VDSL modem with 35b Supervectoring compatibility and VDSL2/ADSL2+ fallback.

Bandwidth Management
Prevent one device using all the bandwidth by bandwidth limit policy, session limit policy, and QoS settings.

DrayDDNS
Free DDNS service to access the router using a fixed hostname of your choice. Learn more

VPN (Virtual Private Network)
Build a secure and private tunnel from the LAN of the Vigor2767 Series to remote offices and teleworkers over the Internet. Learn more

EasyVPN
Secure VPN in Seconds: No Keys, No Configs, Just Login.

Port Knocking
Add a stealth security layer to protect ports from unauthorized access.

Firewall & Content Filter
Filter web pages by URL keywords or web category to block access to insecure or inappropriate content.

URL/IP Reputation
Improve network security by classifying URLs and IPs to control web access and protect against online threats. Learn more

IAM
A solution that manages digital identities, authentication, and access control to ensure the right users or groups have appropriate access to critical resources. Learn more

Hotspot Web Portal
Market your business and communicate with the guests while offering hospitality WLAN. Learn more

Wi-Fi 6 (ax model only)
Feature OFDMA and MU-MIMO technology to improve Wi-Fi efficiency and deliver higher wireless speed.

Mesh (Wireless model only)
Easily link to other VigorAP to expand the wireless network. Learn more

Virtual AP/Switch controller
All-in-one management platform for Vigor2767 Series to maintain and monitor the VigorAPs and VigorSwitches.
[DISPLAY OFF] —– MOBILE VIEW
2.5GbE
Provides higher performance to Wi-Fi 6 AP and other Ethernet devices.
35b Supervectoring Modem
Integrated VDSL modem with 35b Supervectoring compatibility and VDSL2/ADSL2+ fallback.
Bandwidth Management
Prevent one device using all the bandwidth by bandwidth limit policy, session limit policy, and QoS settings.
DrayDDNS
Free DDNS service to access the router using a fixed hostname of your choice. Learn more
VPN (Virtual Private Network)
Build a secure and private tunnel from the LAN of the Vigor2767 Series to remote offices and teleworkers over the Internet. Learn more
EasyVPN
Secure VPN in Seconds: No Keys, No Configs, Just Login.
Port Knocking
Add a stealth security layer to protect ports from unauthorized access.
Firewall & Content Filter
Filter web pages by URL keywords or web category to block access to insecure or inappropriate content.
URL/IP Reputation
Improve network security by classifying URLs and IPs to control web access and protect against online threats. Learn more
IAM
A solution that manages digital identities, authentication, and access control to ensure the right users or groups have appropriate access to critical resources. Learn more
Hotspot Web Portal
Market your business and communicate with the guests while offering hospitality WLAN. Learn more
Wi-Fi 6 (ax model only)
Feature OFDMA and MU-MIMO technology to improve Wi-Fi efficiency and deliver higher wireless speed.
Mesh (Wireless model only)
Easily link to other VigorAP to expand the wireless network. Learn more
Virtual AP/Switch controller
All-in-one management platform for Vigor2767 Series to maintain and monitor the VigorAPs and VigorSwitches.
NAT & Routing Performance
With hardware acceleration, Vigor2767 Series delivers up to 2.3 Gbps aggregate NAT throughput, meeting the demands of business-critical applications while keeping VoIP traffic as the top priority. Additionally, a single 1GbE client can reach up to 950 Mbps, and VDSL2 35b provides up to 300 Mbps to LAN.


Faster Wired Connections
- 4K video streaming
- Online Gaming
- Large file transfers
- Network-attached storage (NAS) devices, etc
Beyond Gigabit
Up to 2.5Gbps internet speed enable the users to fully utilize the available bandwidth
Effortless and Secure VPN Access with EasyVPN
Setting up a VPN can often be complex, involving protocol selection, manual configurations, and troubleshooting, especially for non-technical users. While Vigor routers support advanced VPN protocols such as IPsec, WireGuard, and OpenVPN, traditional setup methods can be time-consuming and daunting.
EasyVPN simplifies this process by offering a streamlined, hassle-free solution for secure remote connectivity. With EasyVPN, users can quickly establish encrypted connections without the need to:
- Manually generate WireGuard keys
- Import OpenVPN configuration files
- Upload certificates
By automating these steps, EasyVPN delivers a fast, secure, and intuitive VPN experience, perfect for businesses and users who want robust protection without the technical complexity.

Stealth Security Protection with Port Knocking
DrayTek’s Port Knocking technology adds an advanced stealth security layer by keeping critical network services completely invisible to unauthorised users. Instead of exposing management ports or VPN services to the public internet, Port Knocking requires a predefined “knock” sequence before access is granted, ensuring that only trusted users can discover and use these services.
By integrating three powerful functions, Port Knocking provides robust protection against port scanning, brute-force attacks, and unauthorised access.
Port Redirection
- Conceal real service ports from the public internet
- Redirect unauthorised requests to non-existent services to prevent detection

Secure Router Management Access
- Allow router management access only after a successful knock sequence or through a secure internal server
- Completely eliminate direct exposure of the management interface to the open internet
VPN Service Control (WAN Binding)
- Keep VPN services invisible until the correct knock sequence is received
- Bind VPN availability to specific WAN interfaces and authorised IP addresses
How It Works
- By default, all protected ports remain closed and undetectable
- After the correct knock sequence is received, selected ports open temporarily for authorised access
- Once the configured time window expires, services automatically return to hidden mode
With DrayTek Port Knocking, your network operates in stealth mode, invisible to attackers yet instantly accessible to authorised administrators and remote users. It is the ideal solution for organisations that demand high-level security without compromising accessibility.
Vigor2767ax 2.5GbE Router with AX3000 (Wi-Fi 6) capacity

Vigor2767ax is a 2×2 dual-band Wi-Fi router that provides 160MHz bandwidth and 1024-QAM modulation to increase wireless data speed greatly. The theoretical speed is up to 3,000Mbps, of which 574Mbps is in the 2.4GHz band and 2,402Mbps in the 5GHz band, making it 2.5 times faster than an 802.11ac 2×2 dual-band router. Equipped with business-grade features, including URL Reputation, Route Policy, App-based QoS, and lots more, Vigor2767ax is perfect for professional smart homes/SOHO users who want to take full control of their network.
OFDMA (Orthogonal Frequency Division Multiple Access) is a core feature of the Wi-Fi 6 certification program. As part of the Wi-Fi 6 standard, OFDMA leverages advanced scheduling mechanisms to optimise performance in congested and complex network environments.
With Wi-Fi 6 gaining widespread adoption across manufacturers and the broader industry, it is increasingly important to evaluate and document the tangible benefits of effective OFDMA implementation, as well as establish reliable methods to measure and quantify its real-world performance impact.
OFDM

OFDMA

MU-MIMO works like multiple trucks delivering goods at the same time. Instead of serving one device after another, it allows the router to transmit data to multiple devices simultaneously, improving overall network capacity and delivering higher speeds for each user.

BSS Colouring is a technique that enhances the coexistence of overlapping Basic Service Sets (BSSs) and enables better spatial reuse within a single channel. Simply put, BSS Colouring helps reduce the co-channel interference commonly seen in legacy Wi-Fi networks.

TWT (Target wake time)
Devices negotiate with the AP for a Target Wake Time (TWT), or joint a TWT broadcast session, and transmit data only when the TWT arrives, thereby reducing power consumption and increase network efficiency.

WPA3 (Wi-Fi Protected Access 3) enhances the security of Wi-Fi networks by addressing vulnerabilities in previous standards (WEP, WPA and WPS2) and introduces new features including stronger authentication, better encryption, and improved protection against attacks such as brute-force password guessing and man-in-the-middle exploits.
DrayTek’s Wi-Fi 6 encryption:
- WEP (64 / 128-bit)
- WPA / WPA2 / WPA3 / OWE
The comparison table below compares security design of Wi-Fi security protocols WEP, WPA, WPA2 and WPA3.
| WEP | WPA | WPA2 | WPA3 | |
|---|---|---|---|---|
| Encryption | RC4 | TKIP / RC4 | AES-CCMP | AES-CCMP / AES-GCMP |
| Session Key | 64/128 bit | 128 bit | 128 bit | 128/256 bit |
| Authentication | Open system, shared key | Pre-shared key | Pre-shared key | AES-CCMP / AES-GCMP |
| Level of Security | Very low | Low | Moderate | High |
| WPA3 |
|---|
| Encryption: AES-CCMP / AES-GCMP |
| Session Key: 128/256 bit |
| Authentication: AES-CCMP / AES-GCMP |
| Level of Security: High |
| WPA2 |
|---|
| Encryption: AES-CCMP |
| Session Key: 128 bit |
| Authentication: Pre-shared key |
| Level of Security: Moderate |
| WPA |
|---|
| Encryption: TKIP / RC4 |
| Session Key: 128 bit |
| Authentication: Pre-shared key |
| Level of Security: Low |
| WEP |
|---|
| Encryption: RC4 |
| Session Key: 64/128 bit |
| Authentication: Open system, shared key |
| Level of Security: Very low |
URL Reputation
URL Reputation is a cloud-based threat intelligence service that adds an extra layer of security to protect LAN clients during their online activities.
With a total of 82 content categories, including 10 security-focused ones, it provides comprehensive and up-to-date protection for both home and business networks.
These categories cover a wide range of areas—from malware, spyware, and adware, to parental controls, business productivity, and social networking—helping to create a safer online environment, enhance employee productivity, and support efficient bandwidth management.

IP Reputation
Every internet communication involves source and destination IP addresses. Cybercriminals often exploit known malicious IPs to launch attacks using various techniques, including:
- Botnets
- TOR nodes and anonymous proxies
- Command-and-Control (C2) servers
- Phishing servers
- Distributed Denial of Service (DDoS) attacks

IP Reputation helps identify and block traffic from these high-risk IP addresses, adding an essential layer of network protection against cyber threats.
Blocking communication with malicious IP addresses is critical for network security. However, relying on static blocklists is no longer effective, as they lack the real-time, predictive intelligence needed to combat evolving threats. The IP Reputation Service addresses this challenge by delivering dynamic, real-time scoring and classification of IP addresses. It enables the automatic blocking of:
- High-risk traffic
- Suspicious proxies
- Malware distributors
- IPs associated with recent malicious activity
The system evaluates IPs based on multiple factors, including infection history, protocol behaviour, and attack frequency. Each IP is assigned a reputation score, which determines whether it should be trusted, monitored, or blocked, ensuring proactive and intelligent network protection.
IAM (Identity and Access Management)
The Vigor2767 Series, powered by the new DrayOS 5, is fully Zero Trust ready!
IAM (Identity and Access Management) is a cybersecurity system that controls user access by managing digital identities, authentication, and authorisation, to ensure correct access to network resources such as applications and devices.

With processes including identifying, authenticating, authorising users or groups, and assigning appropriate levels of access, IAM enhances both security management and the user experience and plays an important role in cloud-based services.
The IAM solution from Vigor2767 is Zero Trust Ready, and allows you to grant and categorize user privileges, create and manage access policies, and define large-scale group policies that integrate multiple filtering rules and traffic-shaping settings.
Users & Groups
- User accounts and user groups allow flexible access level control.
- Existing external authentication server is supported.
- User and MFA protection can be easily configured.

Access Policies
System administrators can create access policies for the local users in this tab. The access policies can be configured based on:
- MAC address filter list
- The allowed / blocked user list
- The login sessions lifetime
Access policies can be combined to create a robust security framework for your system.

Group Policies
Group policies can be configured for predefined local resources such as employees, workstations, network printers, and local servers. Network Firewall and traffic shaping policies can be configured to enhance network security and optimise traffic flows.
Conditional Access Policy
Conditional access policies can be configured to request users to provide multiple forms of authentication before granting appropriate access to a resource.
- Specify a period for the user to re-authenticate
- Restrict access to specific source IP addresses or ranges of IP addresses
- Specify VLAN-based access level in your conditional policies
- Set up time schedules when users are allowed to log-in

Resources Tab
Configure local resources such as IP and Mac addresses for workstations, network printers, PBX systems, NVR systems, servers, etc.
Backup and Restore
Backup or restore router settings such as Users and Groups, Access and Group Policies, etc. A Password protection can be applied before backup or restore.

Seamless Wi-Fi Roaming

Fast & Smooth Handover
Seamlessly switch between access points with intelligent roaming support. Supports both Over-the-DS (via wired backbone) and Over-the-Air handoffs, ensuring reliable connectivity for video calls, voice communications, and real-time applications.
Smarter Assisted Roaming
Configurable signal thresholds and AP steering guide devices to stronger access points and help balance network loads.
Enjoy stable, consistent performance across all devices everywhere.
Always Optimized for Business
From offices to campuses, seamless roaming delivers uninterrupted mobility. Built to provide reliable coverage for the demands of modern workplaces.
Mesh Wi-Fi (Vigor2767ax only)
Vigor2767ax supports up to 7 APs, which can form one or more Wireless Groups. Each group can form Mesh links automatically based on the optimum signal level among the APs and devices.


Unified Mesh & AP Management
The Virtual Controller offers two deployment modes, providing flexible and efficient network management.

Mesh Mode
Automatically forms a self-healing wireless mesh network, with the Vigor2767ax as the Root AP and up to 7 Node APs, delivering easy, scalable, and reliable Wi-Fi coverage.
AP Management Mode
For networks with more than 8 APs, the Virtual Controller switches to AP Management mode, allowing centralised control of up to 20 APs directly through the router’s interface.
Seamless Mesh Role Assignment
Seamless Mesh Role Assignment
When powered on, devices automatically discover each other and assign roles as Root or Node Aps, no manual setup required. This streamlined process enables rapid mesh network formation with optimised coverage and self-healing reliability.
Central Switch Manager (SWM)
The Central Switch Manager (SWM) provides a comprehensive solution for simplifying network administration. It automatically detects and manages all compatible VigorSwitches from a single, centralised interface, eliminating the need to configure each device individually. Administrators can efficiently push configurations to multiple switches and monitor their real-time status to ensure network stability.
SWM also streamlines advanced management tasks, allowing easy implementation of VLAN segmentation and Quality of Service (QoS) policies. This consolidated approach reduces maintenance time and boosts the overall efficiency and reliability of your network infrastructure
SWM

The Vigor2767 Series can function as a master controller, managing and monitoring up to 5 switches. It also provides full visibility into powered devices (PDs) connected behind the switches, such as IP cameras and access points.
Device Management

Monitor the status, firmware version, and uptime of all managed switches in real time.
Port Profile

Create multiple port profiles to easily configure PoE, VLAN, QoS, and other settings across selected switches.
Maintenance

Easily perform configuration backups and restores, remote reboots, or factory resets.
Software Management – VigorACS 3
- Zero Touch Deployment & Provisioning
- Auto VPN
- Interface Quality & SLA
- VoIP Optimization & Monitoring
- Application Visibility
- Application Based SD-WAN Policy
- Customized Hotspot Page with Multilingual
- Hotspot Clients Analytics
- ACS Server Load Balancing / Failover

In-the-Box
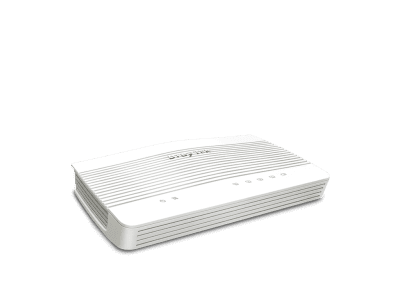
Vigor2767 Series

2 x Antennas
(ax models)

RJ-45 Cable
(Ethernet)

RJ-11 to RJ-11 Cable (Annex A)

Power Adaptor

Quick Start Guide
Models
| Model | Vigor2767 | Vigor2767ax | Vigor2767ax-4G |
|---|---|---|---|
| Product | |  |  |
| VDSL2 35b/ ADSL2/2+ | |||
| Selectable Gigabit WAN/LAN | 1 x 2.5 GbE | 1 x 2.5 GbE | 1 x 2.5 GbE |
| 4G LTE | 2 x USB 2.0 | 2 x USB 2.0 | 2 x nano SIM slots (SIM slot 2 for Failover) & eSIM 1 x USB 2.0 |
| Wireless WAN | |||
| Gigabit LAN | 3 | 3 | 3 |
| VPN Tunnels | 16 | 16 | 16 |
| Wireless LAN | Wi-Fi 6, AX3000 | Wi-Fi 6, AX3000 | |
| Wi-Fi Antenna | 2.7dBi for 5GHz 2.6dBi for 2.4GHz | 2.7dBi for 5GHz 2.6dBi for 2.4GHz | |
| VoIP (2xFXS) |
Specifications
Performance (gDisplayOff)
| Performance | |
|---|---|
| NAT Session | 50,000 |
| Max. NAT (Mbps) | 2300 |
[DISPLAY OFF] —– MOBILE VIEW
| Performance |
|---|
| NAT Session: 50K |
| Max. NAT (Mbps): 2300 |
WAN (gDisplayOff)
| WAN | |
|---|---|
| xDSL | 1 |
| Selectable Gigabit WAN/LAN | 1 x 2.5 GbE |
| VDSL Standards | ITU-T G.993.1 (VDSL), ITU-T G.993.2 Annex A/B/M/Q, G.997.1 |
| VDSL2 Profile | 8a, 8b, 8c, 8d, 12a, 12b, 17a, 30a, 35b |
| ADSL Standards | ITU-T G.992.1(G.dmt), T1.413 Issue 2 |
| Band Plan | 998, 997 |
| Cellular (via USB) | 2 |
| Wireless WAN (2.4GHz + 5GHz) | (ax model only) |
[DISPLAY OFF] —– MOBILE VIEW
| WAN | |
|---|---|
| xDSL: 1 | |
| Selectable Gigabit WAN/LAN: 1 x 2.5 GbE | |
| VDSL Standards: ITU-T G.993.1 (VDSL) ITU-T G.993.2 Annex A/B/M/Q G.997.1 | |
| VDSL2 Profile: 8a, 8b, 8c, 8d, 12a, 12b, 17a, 30a, 35b | |
| ADSL Standards: ITU-T G.992.1(G.dmt) T1.413 Issue 2 | |
| Band Plan: 998, 997 | |
| Cellular (via USB): 2 | |
| Wireless WAN: (2.4GHz + 5GHz) (ax model only) | |
Internet Connection (gDisplayOff)
| Internet Connection | |
|---|---|
| IPv4 | PPPoE, DHCP, Static IP |
| IPv6 | PPP, DHCPv6, Static IPv6, TSPC, 6rd, 6in4 Static Tunnel |
| 802.1p/q Multi-VLAN Tagging | |
| Failover | |
| Connection Detection | ARP, Ping |
| WAN Data Budget | |
| Dynamic DNS | |
| DrayDDNS | |
[DISPLAY OFF] —– MOBILE VIEW
| Internet Connection | |
|---|---|
| IPv4: PPPoE, DHCP, Static IP | |
| IPv6: PPP, DHCPv6, Static IPv6, TSPC, 6rd, 6in4 Static Tunnel | |
| 802.1p/q Multi-VLAN Tagging | |
| Failover | |
| Connection Detection: ARP, Ping | |
| WAN Data Budget | |
| Dynamic DNS | |
| DrayDDNS | |
LAN (gDisplayOff)
| LAN | |
|---|---|
| Fixed LAN (RJ-45, GbE) | 3 |
| LAN Subnet | 4 |
| VLAN | 802.1q Tag-based VLAN |
| Max. Number of VLAN | 8 |
| DHCP Server | Multiple IP Subnet, Custom DHCP Options, Bind-IP-to-MAC |
| Wired 802.1x Authentication | |
| Port Mirroring | |
| Local DNS Server | |
| Conditional DNS Forwarding | |
| Hotspot Web Portal (Profile No.) | 2 |
| Hotspot Authentication | Click-Through, Social Login, SMS PIN, RADIUS, External Portal Server |
[DISPLAY OFF] —– MOBILE VIEW
| LAN | |
|---|---|
| Fixed LAN (RJ-45, GbE): 3 | |
| LAN Subnet: 4 | |
| VLAN: 802.1q Tag-based VLAN | |
| Max. Number of VLAN: 8 | |
| DHCP Server: Multiple IP Subnet, Custom DHCP Options, Bind-IP-to-MAC | |
| Wired 802.1x Authentication | |
| Port Mirroring | |
| Local DNS Server | |
| Conditional DNS Forwarding | |
| Hotspot Web Portal (Profile No.): 2 | |
| Hotspot Authentication: Click-Through, Social Login, SMS PIN, RADIUS, External Portal Server | |
Wireless LAN (ax model) (gDisplayOff)
| Wireless LAN (ax model) | |
|---|---|
| 2.4GHz WLAN | 802.11ax 2×2 MIMO |
| 5GHz WLAN | 802.11ax 3×3 MU-MIMO |
| Wi-Fi Antenna (External) | 2 |
| Wi-Fi Antenna (Internal) | 1 |
| 2.4GHz Antenna Gain | 2.6dBi |
| 5GHz Antenna Gain | 2.7dBi |
| 2.4GHz Max. Link Rate | 574Mbps |
| 5GHz Max. Link Rate | 2402Mbps |
| Max. Number of SSIDs (per band) | 8 (4) |
| Security Mode | OWE, WEP, WPA, WPA2, WPA2/WPA, WPA3, WPA3/WPA2 |
| Authentication | Pre-Shared Key, 802.1x |
| WiFi 6 | |
| OFDMA | |
| Roaming | Assisted Roaming |
| WPS | WPS Button, PIN Code |
| WDS | Repeater |
| Access Control | Access List, Client Isolation, Hide SSID, Wi-Fi Scheduling |
| AirTime Fairness | |
| Band Steering | |
| WMM | |
| Mesh (5GHz only) | Root |
[DISPLAY OFF] —– MOBILE VIEW
| Wireless LAN (ax model) | |
|---|---|
| 2.4GHz WLAN: 802.11ax 2×2 MIMO | |
| 5GHz WLAN: 802.11ax 3×3 MU-MIMO | |
| Wi-Fi Antenna (External): 2 | |
| Wi-Fi Antenna (Internal): 1 | |
| 2.4GHz Gain: 2.6dBi | |
| 5GHz Gain: 2.7dBi | |
| 2.4GHz Max. Link Rate: 574Mbps | |
| 5GHz Max. Link Rate: 2402Mbps | |
| Max. Number of SSIDs (per band): 8 (4) | |
| Security Mode: OWE WEP WPA WPA2 WPA2/WPA WPA3 WPA3/WPA2 | |
| Authentication: Pre-Shared Key, 802.1x | |
| WiFi 6 | |
| OFDMA | |
| Roaming: Assisted Roaming | |
| WPS: WPS Button, PIN Code | |
| WDS: Repeater | |
| Access Control: Access List Client Isolation Hide SSID WLAN Scheduling | |
| AirTime Fairness | |
| Band Steering | |
| WMM | |
| Mesh (5GHz only): Root | |
Other Ports (gDisplayOff)
| Other Ports | |
|---|---|
| USB | 2 |
| USB Type | 2.0 |
| USB Application | User Management, File Explorer, FTP File Sharing, Device Status, Printer Server, Temperature Sensor, USB WAN |
| SMB File Sharing (Requires external storage) | |
[DISPLAY OFF] —– MOBILE VIEW
| Other Ports | |
|---|---|
| USB: 2 | |
| USB Type: 2.0 | |
| USB Application: User Management File Explorer FTP File Sharing Device Status Printer Server Temperature Sensor USB WAN | |
| SMB File Sharing (Requires external storage) | |
Networking (gDisplayOff)
| Networking | |
|---|---|
| Routing | IPv4 Static Routing, IPv6 Static Routing, Policy Route, Inter-VLAN Route, RIP v1/v2, OSPF(V2/V3), BGP |
| Policy-based Routing | Protocol, IP Address, Port |
| DNS Security (DNSSEC) | |
| IGMP | IGMP v2/v3, IGMP Proxy, IGMP Snooping & Fast Leave |
| Local RADIUS server | |
[DISPLAY OFF] —– MOBILE VIEW
| Networking | |
|---|---|
| Routing: IPv4 Static Route IPv6 Static Route Policy Route Inter-VLAN Route RIP v1/v2 OSPF(V2/V3) BGP | |
| Policy-based Routing: Protocol IP Address Port | |
| DNS Security (DNSSEC): | |
| IGMP: IGMP v2/v3 IGMP Proxy IGMP Snooping & Fast Leave | |
| Local RADIUS server: | |
Bandwidth Management (gDisplayOff)
| Bandwidth Management | |
|---|---|
| Traffic Shaping Policy | |
| IP-based Bandwidth Limit | |
| IP-based Session Limit | |
| QoS (Quality of Service) | IP Address, Port, Application |
| APP QoS | |
| Default Policy | |
| VoIP Prioritization | |
[DISPLAY OFF] —– MOBILE VIEW
| Bandwidth Management | |
|---|---|
| Traffic Shaping Policy | |
| IP-based Bandwidth Limit | |
| IP-based Session Limit | |
| QoS (Quality of Service): IP Address, Port, Application | |
| APP QoS | |
| Default Policy | |
| VoIP Prioritization | |
NAT (gDisplayOff)
| NAT | |
|---|---|
| Port Forwarding | |
| DMZ Host | |
| Port Trigger | |
| ALG (Application Layer Gateway) | SIP, RTSP, FTP, H.323 |
| UPnP | |
[DISPLAY OFF] —– MOBILE VIEW
| NAT | |
|---|---|
| Port Forwarding | |
| DMZ Host | |
| Port Trigger | |
| ALG (Application Layer Gateway): SIP, RTSP, FTP, H.323 | |
| UPnP | |
Management (gDisplayOff)
| Management | |
|---|---|
| Local Service | HTTP, HTTPS, Telnet, SSHv2, FTP, TR-069 |
| Config Backup/Restore | |
| Firmware Upgrade | WUI, TFTP, TR-069 |
| Role-based Privilege | |
| Access Control | Access List, Brute Force Protection |
| Notification Alert | SMS, E-mail |
| SNMP | v1, v2c, v3 |
| Syslog | |
| Virtual AP Controller (Device up to) | 20 |
| Mesh (Number of manageable APs) | 7 (ax model only) |
| Virtual Switch Controller | 5 |
| Managed by VigorACS | Since f/w v5.3.5 |
[DISPLAY OFF] —– MOBILE VIEW
| Management | |
|---|---|
| Local Service: HTTP, HTTPS, Telnet, SSH v2, FTP, TR-069 | |
| Config Backup / Restore | |
| Firmware Upgrade: WUI, TFTP, TR-069 | |
| Role-based Privilege | |
| Access Control: Access List, Brute Force Protection | |
| Notification Alert: SMS, E-mail | |
| SNMP: v1, v2c, v3 | |
| Syslog | |
| Virtual AP Controller (Device up to): 20 x VigorAPs | |
| Mesh (Number of manageable APs): 7 (ax model only) | |
| Virtual Switch Controller: 5 | |
| VigorACS Management: Since f/w v5.3.5 | |
Security (gDisplayOff)
| Security | |
|---|---|
| URL/IP Reputation | |
| Firewall Filter | IP, Content, Traffic |
| Port Knocking | |
| Defense Setup | ARP Spoofing, IP Spoofing |
| MAC Filtering Profile | |
| IPv6 Address Security | |
[DISPLAY OFF] —– MOBILE VIEW
| Security | |
|---|---|
| URL/IP Reputation | |
| Firewall Filter: IP, Content, Traffic | |
| Port Knocking | |
| Defense Setup: ARP Spoofing, IP Spoofing | |
| MAC Filtering Profile | |
| IPv6 Address Security | |
IAM (gDisplayOff)
| IAM | |
|---|---|
| Users & Groups | |
| Access Policies | |
| Group Policies | |
| Conditional Access Policy | |
| Resources | |
| Account Status | |
| Backup and Restore | |
[DISPLAY OFF] —– MOBILE VIEW
| IAM | |
|---|---|
| Users & Groups | |
| Access Policies | |
| Group Policies | |
| Conditional Access Policy | |
| Resources | |
| Account Status | |
| Backup and Restore | |
VPN (gDisplayOff)
| VPN | |
|---|---|
| Site-to-Site VPN | |
| Teleworker VPN | |
| EasyVPN | |
| Protocols | IPsec, IKEv1/IKEv2, IKEv2-EAP, IPsec-XAuth, OpenVPN, WireGuard |
| Max. VPN Tunnels | 16 |
| IPsec VPN Throughput (AES 256 bits) | 300 Mbps (single-directional) |
| WireGuard VPN Throughput | 50 Mbps (single-directional) |
| User Authentication | Local, RADIUS, TACACS+, mOTP, TOTP |
| IKE Authentication | Pre-Shared Key, X.509 |
| IPsec Authentication | SHA-1, SHA-256 |
| Encryption | DES, 3DES, AES |
| Single-Armed VPN | |
| NAT-Traversal (NAT-T) | |
| VPN Connection Status | |
| Backup & Restore | |
[DISPLAY OFF] —– MOBILE VIEW
| VPN | |
|---|---|
| Site-to-Site VPN | |
| Teleworker VPN | |
| EasyVPN | |
| Protocols: IPsec IKEv1/IKEv2 IKEv2-EAP IPsec-XAuth OpenVPN WireGuard | |
| Max. VPN Tunnels: 16 | |
| IPsec VPN Throughput (AES 256 bits): 300 Mbps (single-directional) | |
| WireGuard VPN Throughput: 50 Mbps (single-directional) | |
| User Authentication: Local RADIUS TACACS+ mOTP TOTP | |
| IKE Authentication: Pre-Shared Key, X.509 | |
| IPsec Authentication: SHA-1, SHA-256 | |
| Encryption: DES 3DES AES | |
| Single-Armed VPN | |
| NAT-Traversal (NAT-T) | |
| VPN Connection Status | |
| Backup & Restore | |
Monitoring (gDisplayOff)
| Monitoring | |
|---|---|
| Clients List | |
| Log Center | |
| Wireless Information | (ax model only) |
| WAN | |
| ARP Table | |
| Route Table | |
| DHCP Table | |
| IPv6 TSPC Status | |
| IPv6 Neighbor Table | |
| LLDP Neighbors | |
| DNS Cache Table | |
| DSL Status | |
| Remote DSL Status | |
| PPPoE Pass-Through | |
| Session Table | |
| Running Service | |
| Port Knocking Status | |
[DISPLAY OFF] —– MOBILE VIEW
| Monitoring | |
|---|---|
| Clients List | |
| Log Center | |
| Wireless Information (ax model only) | |
| WAN | |
| ARP Table | |
| Route Table | |
| DHCP Table | |
| IPv6 TSPC Status | |
| IPv6 Neighbor Table | |
| LLDP Neighbors | |
| DNS Cache Table | |
| DSL Status | |
| Remote DSL Status | |
| PPPoE Pass-Through | |
| Session Table | |
| Running Service | |
| Port Knocking Status | |
Physical (gDisplayOff)
| Physical | |
|---|---|
| Power Supply | Vigor2767: DC 12V @ 1.15A Vigor2767ax: DC 12V @ 1.8A |
| Max. Power Consumption | Vigor2767: 13.7 watts Vigor2767ax: 21.6 watts |
| Dimension | 207mm x 131mm x 42mm |
| Weight | Vigor2767: 460g Vigor2767ax: 510g |
| Operating Temperature | 0 to 45°C |
| Storage Temperature | -25 to 70°C |
| Operating Humidity (non-condensing) | 10 to 90% |
[DISPLAY OFF] —– MOBILE VIEW
| Physical | |
|---|---|
| Power Supply: DC 12V @ 1.15A (Vigor2767) DC 12V @ 1.8A (Vigor2767ax) | |
| Max. Power Consumption: 13.7 watts (Vigor2767) 21.6 watts (Vigor2767ax) | |
| Dimension: 207mm x 131mm x 42mm | |
| Weight: 460g (Vigor2767) 510g (Vigor2767ax) | |
| Operating Temperature: 0 to 45°C | |
| Storage Temperature: -25 to 70°C | |
| Operating Humidity (non-condensing): 10 to 90% |
Note :
- All specifications are subject to change without notice.
- The throughput figures are maximum, based on DrayTek internal testing with optimal conditions. The actual performance may vary depending on the different network conditions and applications activated.


